Coinbase and the Limits of European Financial Supervision
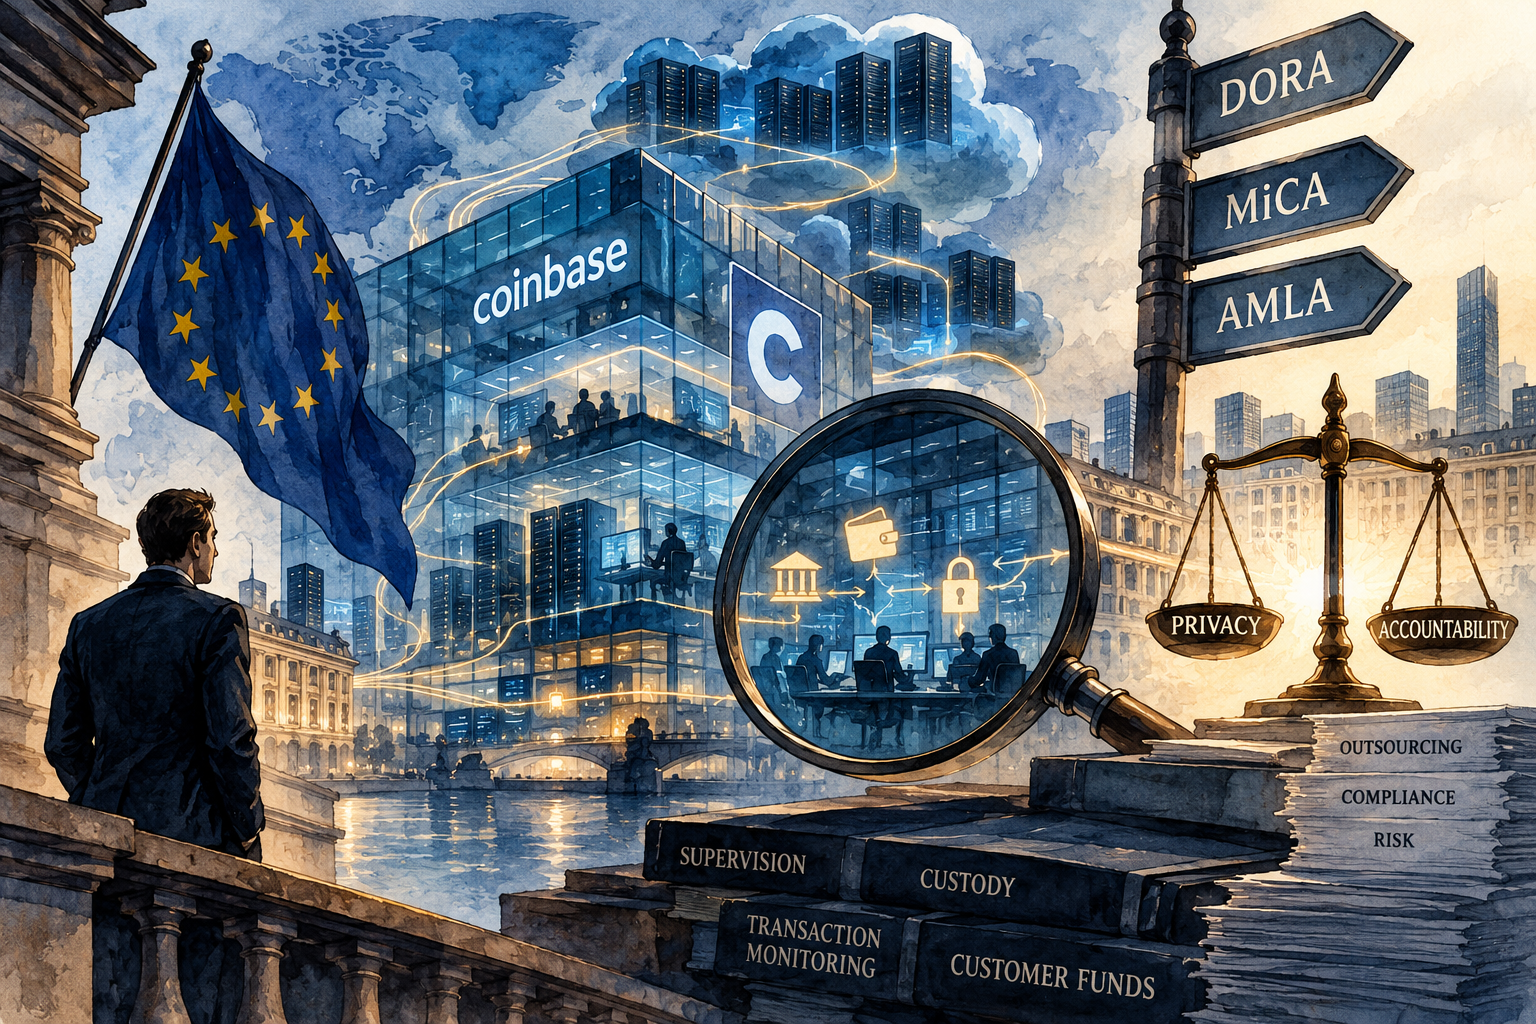
When financial infrastructure becomes less visible, accountability becomes harder to establish.
The €3.25 million penalty announced against Coinbase Ireland Limited on 22 October 2026 exposes a structural tension in European financial supervision. As institutions become increasingly digital, cross-border and dependent on outsourced infrastructure, regulators must ensure that legal accountability remains matched by operational control.
The case reaches beyond cryptocurrency. It raises six questions about the effectiveness of Europe’s financial safeguards.
🟦 What went wrong at Coinbase Ireland?
The Central Bank of Ireland sanctioned Coinbase Ireland Limited for breaches of safeguarding and outsourcing requirements between November 2020 and August 2025. The settlement remains subject to confirmation by the Irish High Court.
Coinbase Ireland relied heavily on functions outsourced to its US parent group but lacked sufficient local expertise and independent oversight. Weaknesses in system design and control testing left safeguarding accounts underfunded for extended periods.
Coinbase maintains that customers suffered no financial losses and that the historical deficiencies have been resolved.
The regulatory failure was preventive: safeguards intended to protect customer funds proved inadequate even though the platform continued operating.
🟦 Is this an isolated breach or a wider control problem?
In November 2025, the Central Bank imposed a separate €21.5 million penalty on Coinbase Europe Limited for anti-money-laundering monitoring failures. More than 30 million transactions, worth over €176 billion, were not properly monitored during a twelve-month period.
The cases concern different legal entities and regulatory breaches, but expose two critical vulnerabilities: safeguarding customer assets and monitoring financial flows.
Both depend on internal controls that customers cannot independently verify.
The broader concern is whether platform-scale financial institutions have expanded operational complexity faster than their governance systems can effectively oversee it.
🟦 Are financial institutions becoming invisible to supervision?
European financial services increasingly operate through distributed infrastructure. Customers may contract with an EU-regulated entity while critical technology, processing and compliance functions operate elsewhere.
Outsourcing creates efficiency but can separate legal accountability from practical control.
In the Coinbase Ireland case, regulatory responsibility remained in Ireland while important safeguarding functions depended on arrangements within the US-based group.
European supervision cannot rely on contractual assurances alone. Regulated entities must possess the expertise and authority to test, challenge and independently oversee critical outsourced functions.
The challenge is not simply access to information, but whether regulators and local management can verify how financial infrastructure actually operates.
🟦 Where does duty of care end and financial gatekeeping begin?
Financial institutions must protect customer assets, execute legitimate transactions, respect confidentiality and identify financial-crime risks.
These are distinct legal obligations, sometimes involving competing interests.
Not every unusual transaction justifies intervention. Banks and payment institutions cannot indiscriminately freeze accounts or treat every warning as evidence of fraud.
But the absence of proven criminal activity does not automatically establish that an institution responded appropriately to relevant risk signals.
The decisive questions are what the institution knew, when it knew it and whether its response met the applicable legal requirements.
Effective gatekeeping depends on documented risk assessment, proportionate intervention and functioning internal escalation—not merely formal compliance procedures.
🟦 Does financial privacy create an accountability gap?
Financial confidentiality protects customers against unjustified disclosure. Yet it also creates substantial information asymmetry.
Individuals questioning an institution’s conduct may have limited access to transaction records, internal compliance assessments or supervisory communications. Third parties may have no entitlement to that information at all.
Regulators possess statutory investigative powers, but affected individuals cannot necessarily determine whether their warnings were adequately assessed.
Privacy is therefore not a barrier to regulatory supervision. It can, however, complicate private accountability and legal challenges.
Europe must preserve financial confidentiality while ensuring that institutional decisions remain independently reviewable through appropriate supervisory and legal mechanisms.
🟦 Can Europe’s supervisory architecture keep pace?
The EU is strengthening its framework. DORA addresses digital operational resilience and ICT dependencies. MiCA harmonises crypto-asset regulation. AMLA is preparing to begin direct supervision of selected high-risk financial institutions in 2028.
These initiatives address different dimensions of financial oversight, but share a central challenge: increasingly complex institutions require demonstrable operational control.
Additional regulation cannot compensate for inadequate technical expertise, weak internal governance or ineffective supervision of outsourced functions.
Nor does a financial licence establish that every critical system operates as intended.
Europe’s supervisory effectiveness will ultimately depend on its ability to identify structural weaknesses before they persist for years—or translate into financial harm.
The Altair Signal
The Coinbase enforcement actions expose a gap between legal accountability and operational control.
As financial infrastructure becomes more complex and cross-border, European supervision must move beyond formal compliance towards independent operational verification.
The decisive test is not how extensively financial institutions are regulated, but whether their critical operations remain controllable, verifiable and accountable.
Image credit
Illustration: Altair Media / AI-generated editorial artwork.
Image caption
As financial infrastructure becomes increasingly complex and less visible, European regulators face a growing challenge: ensuring that legal accountability is matched by effective operational control.
